Defending Systems.
Exploiting Flaws.
I specialize in offensive security, infrastructure hardening, and automated threat detection—helping organizations fortify their digital perimeters before attackers strike.
Host is up (0.012s latency).
[✓] SIEM Integration: Splunk Operational
[!] Threat Matrix: 0 Critical, 0 High Vulnerabilities Active
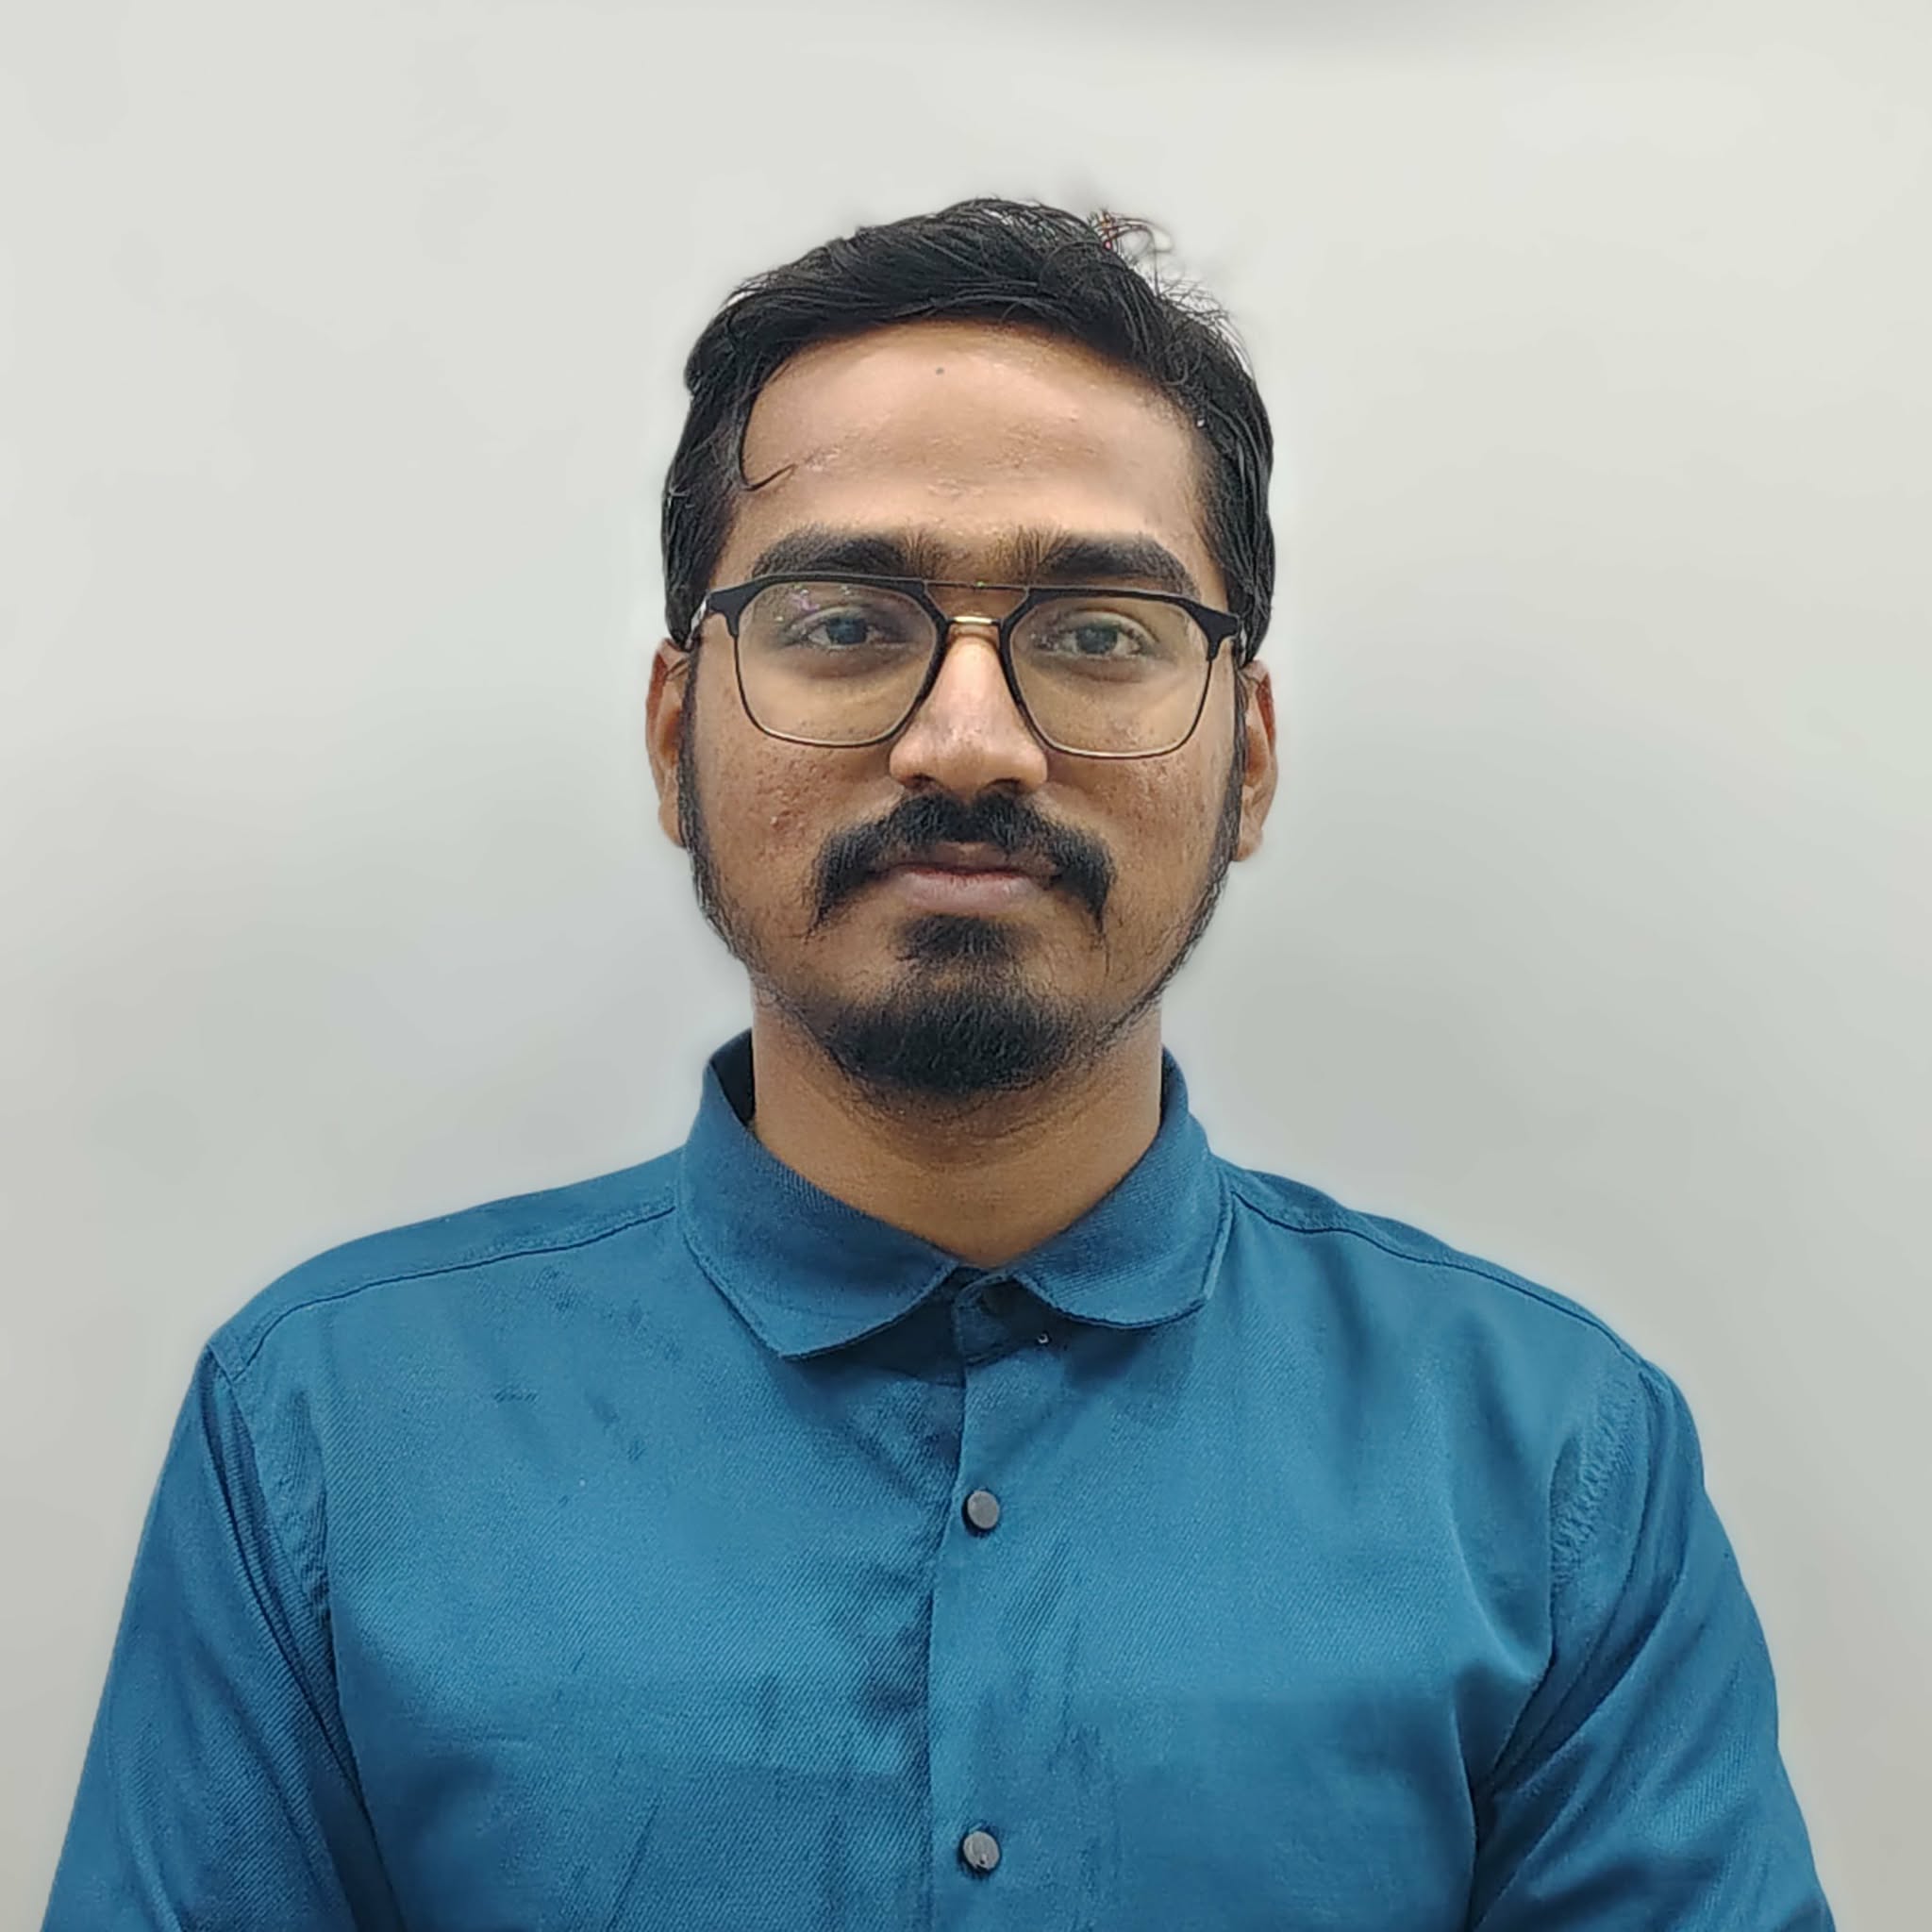
Operator Profile
Abu Jawad
I am a dedicated Cybersecurity Specialist bridging the gap between offensive testing and defensive infrastructure hardening. With a passion for uncovering vulnerabilities before they are exploited, I navigate complex networks to ensure robust security postures.
My expertise spans across Blue Teaming (SIEM architecture, incident response, and threat hunting), Red Teaming (web/API penetration testing and OSINT), and IT Infrastructure (Linux server hardening, virtualization, and networking).
Whether I am analyzing malicious traffic with Wireshark, dissecting an API for logical flaws, or writing custom Wazuh detection rules, my goal remains the same: building resilient systems that withstand sophisticated cyber threats.
Core Expertise
Security Engineering &
Offensive Defense
Comprehensive security assessments, infrastructure hardening, and rapid incident mitigation designed for modern enterprise tech stacks.
Penetration Testing
Black-box and white-box security audits on web apps, APIs, and cloud infrastructure to identify zero-days and vulnerabilities.
- OWASP Top 10 Audit
- API & Microservice PenTesting
- Exploit PoC & Remediation
SOC & Incident Response
Real-time threat monitoring, SIEM log aggregation (Splunk/ELK), malware analysis, and active intrusion containment.
- Log Analysis & Threat Hunting
- Automated Alert Rules
- Post-Breach Forensics
Infrastructure Management
Architecting and managing robust virtualization and network environments by advanced routing and firewalls, observability solutions.
- Proxmox / KVM Virtualization
- MikroTik & IPFire Routing
- Zabbix Infrastructure Monitoring
Capabilities & Experience
Security Operations
Blue Team / Defensive Security
- ▹ Build a SIEM dashboard to monitor failed login attempts using Wazuh custom rules and alerts.
- ▹ Detect and investigate brute-force attacks through security log analysis.
- ▹ Develop endpoint detection rules based on CrowdStrike and Microsoft Defender concepts.
- ▹ Harden Linux servers according to CIS Benchmark recommendations.
- ▹ Analyze and monitor network traffic using Wireshark.
- ▹ Develop a SOC alert-triage workflow and checklist using Wazuh.
- ▹ Implement File Integrity Monitoring (FIM) to detect unauthorized file changes.
- ▹ Configure and manage basic firewall rules using iptables, OpenWrt, and IPFire.
Red Team / Offensive Security
- ▹ Write detailed Capture-the-Flag (CTF) walkthroughs and technical write-ups.
- ▹ Perform web application security testing in intentionally vulnerable environments (bWAPP, Beebox, DVWA, OWASP Juice Shop).
- ▹ Identify and exploit security misconfigurations in controlled lab environments.
- ▹ Perform API security testing in vulnerable API platforms such as DVAPI and crAPI.
- ▹ Conduct OSINT investigations using publicly available information.
- ▹ Produce professional security assessment and penetration testing reports.
IT Infrastructure, Systems & Network Security
- ▹ Perform vulnerability assessments and scans using Nessus.
- ▹ Deploy and configure network and infrastructure monitoring solutions such as Zabbix.
- ▹ Diagnose and recover systems from disk, boot, and OS failures using tools like Hiren's BootCD PE & MediCat.
- ▹ Install, configure, and optimize Linux and other operating systems on a wide range of hardware.
- ▹ Configure and automate MikroTik routers and network devices.
- ▹ Deploy and configure routers and firewall platforms, including OpenWrt, MikroTik, and IPFire.
- ▹ Customize Linux desktop environments, particularly KDE Plasma, for a polished and user-friendly experience.
- ▹ Manage Android devices using ADB, including file push/pull operations, debugging, and screen mirroring.
- ▹ Deploy and manage applications using Docker containers.
- ▹ Work with virtualization technologies such as QEMU/KVM and Proxmox at foundational and intermediate levels.
Let's secure
your infrastructure.
Need a security audit, penetration test, or incident responder? Send details regarding your scope and timeline.
Secure Email (PGP Available)
zawad.abu@protonmail.comLocation / Availability
Global Remote & Emergency On-Call
Hello! I'm Abu Jawad. Need a security audit or have a question about my capabilities?